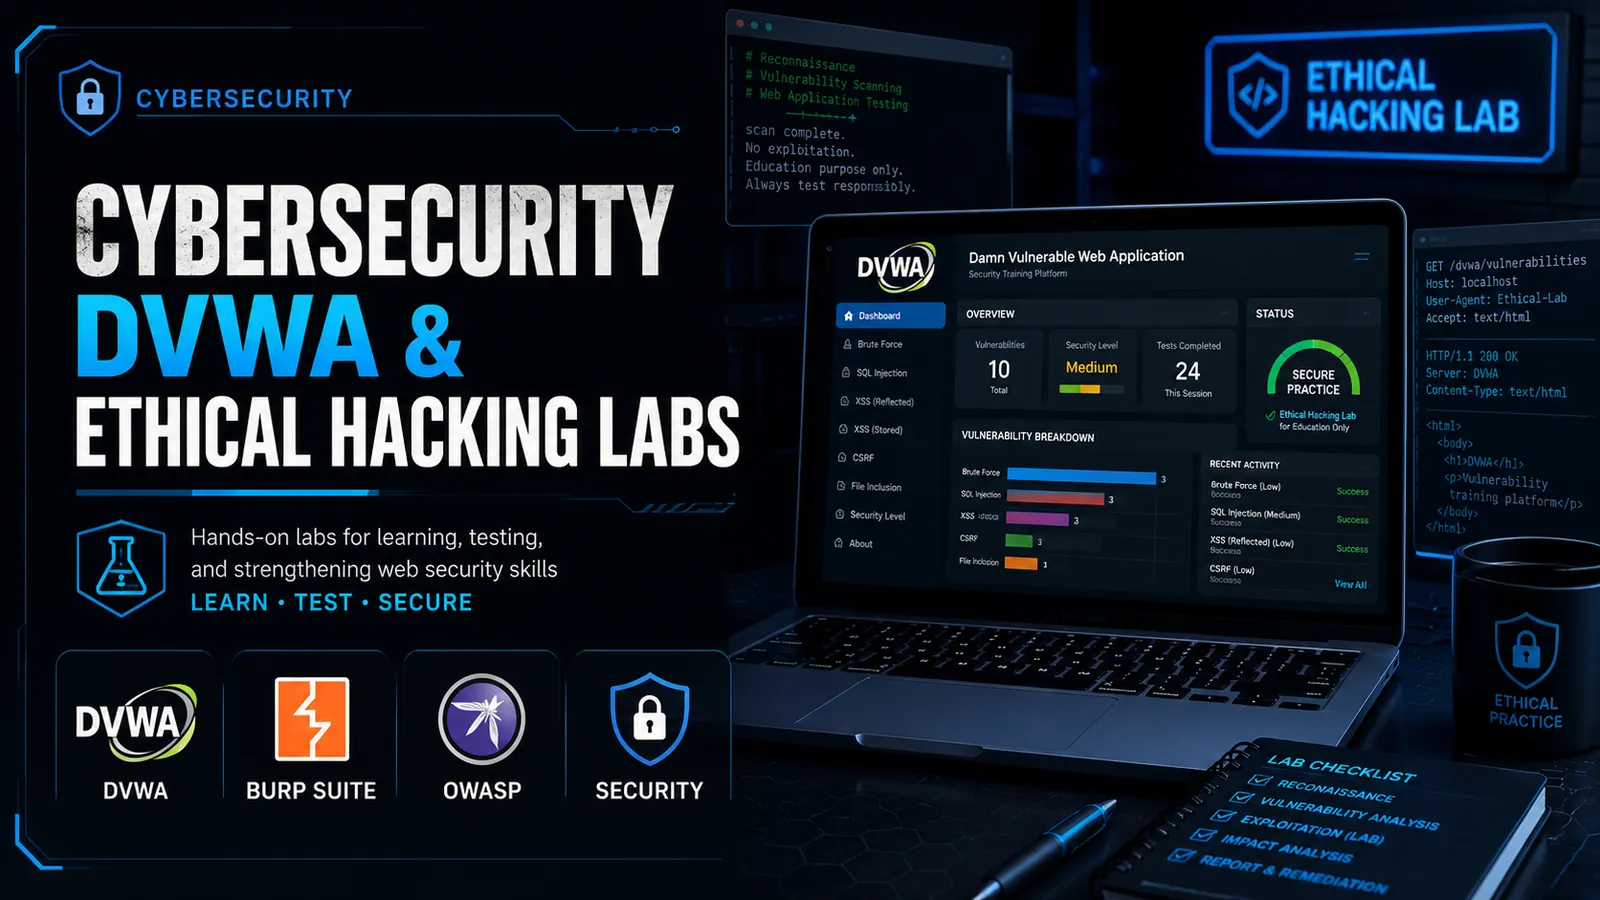
On the security side I test web applications against OWASP-style weaknesses (SQL injection, XSS, CSRF, weak sign-in, unsafe uploads) using the same workflow as my DVWA and Burp Suite labs, and write up every finding with its risk and how to fix it. I only test systems with the owner's written permission.
On the e-commerce side I set up and grow Shopify stores, as with Family Haven: product research, store pages, policies, SEO content and ad testing.
What you get
- A written security report with risk ratings and fixes
- A retest once the fixes are in
- Shopify store setup, product pages and policies
- SEO content and ad campaign testing
Who it suits
Small businesses and online stores that want to sell more without taking on avoidable risk.
How I work
Agree the scope and written permission
Test, or audit the store
Report
findings, risks and fixes in plain language
Retest and follow-up