Cybersecurity DVWA & Ethical Hacking Labs
Hands-on cybersecurity labs using DVWA, Burp Suite, OWASP concepts and professional reporting practice.
Project Description
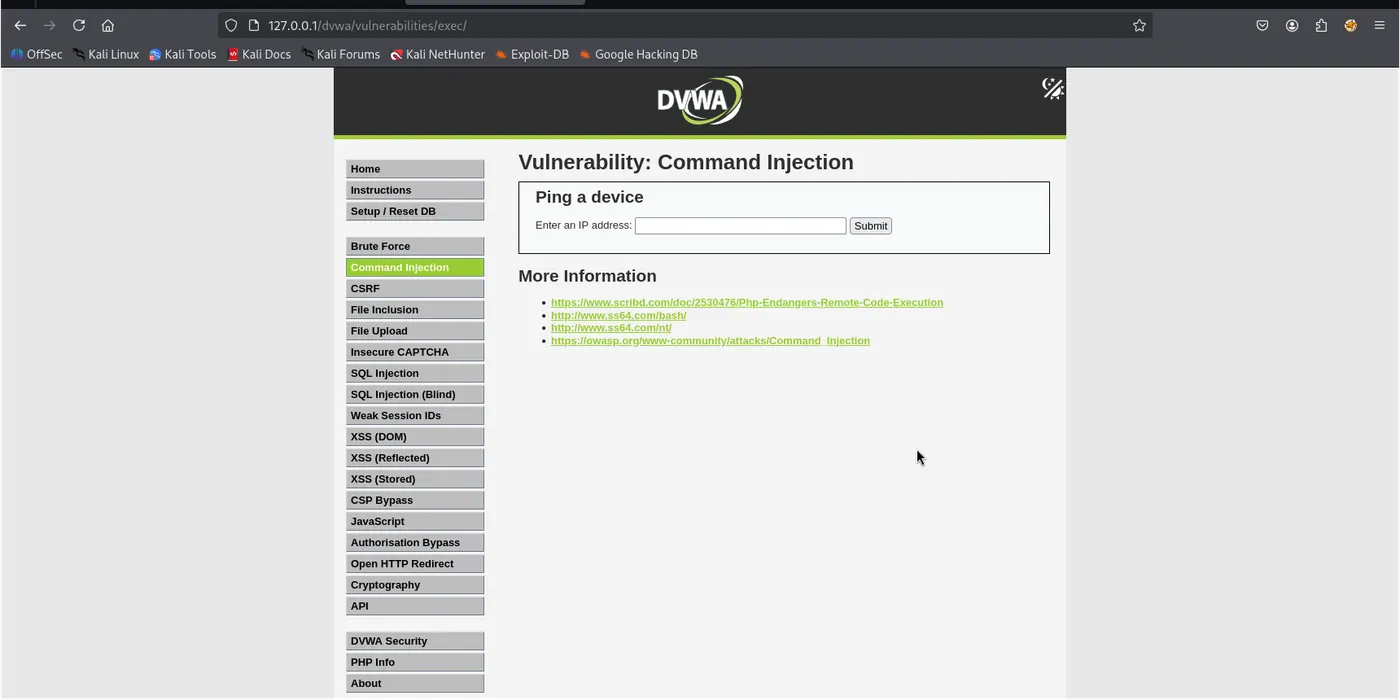
This project is a controlled ethical hacking lab using DVWA and related web security tools to practise vulnerability discovery, exploitation and remediation. DVWA is a deliberately vulnerable web application designed for legal security training. OWASP Top 10 provides a widely recognised framework for common web application security risks, and Burp Suite is a common tool for web penetration testing.
Problem
Students and junior security professionals need a safe environment to practise security testing without attacking real systems. Real websites cannot be tested without permission, so controlled labs are essential.
Solution
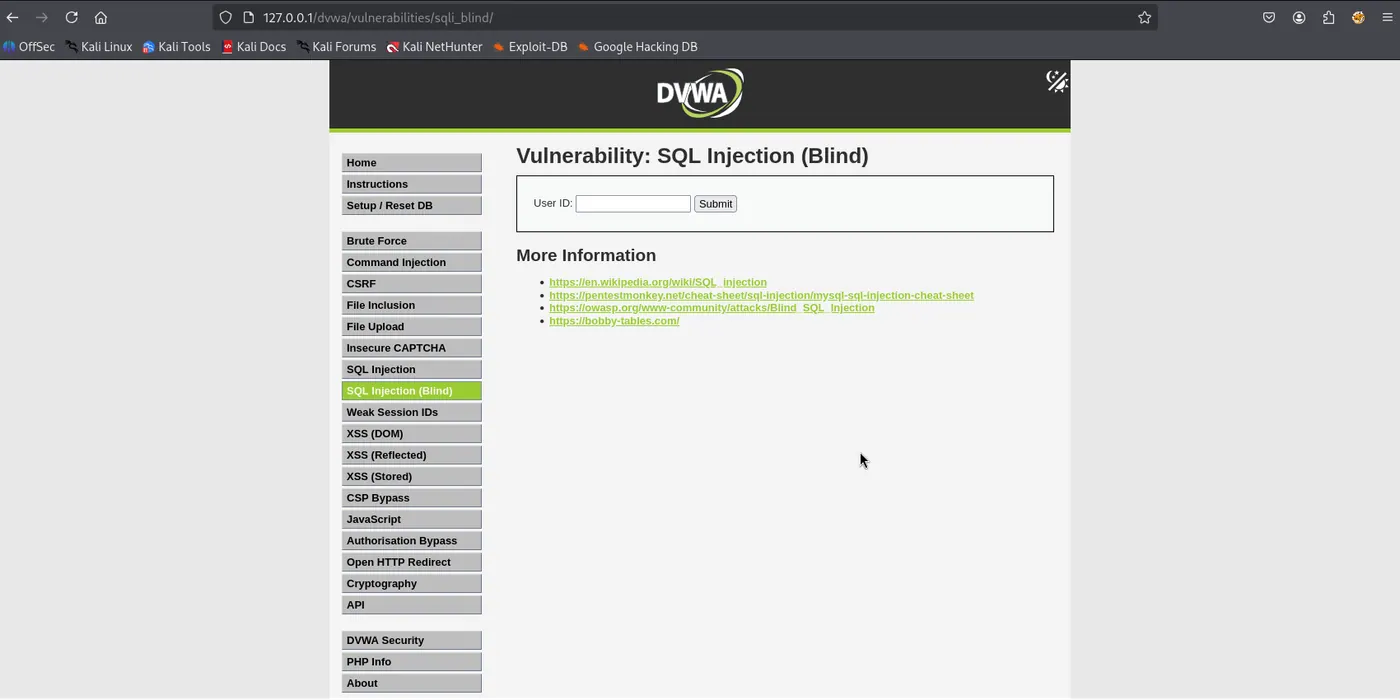
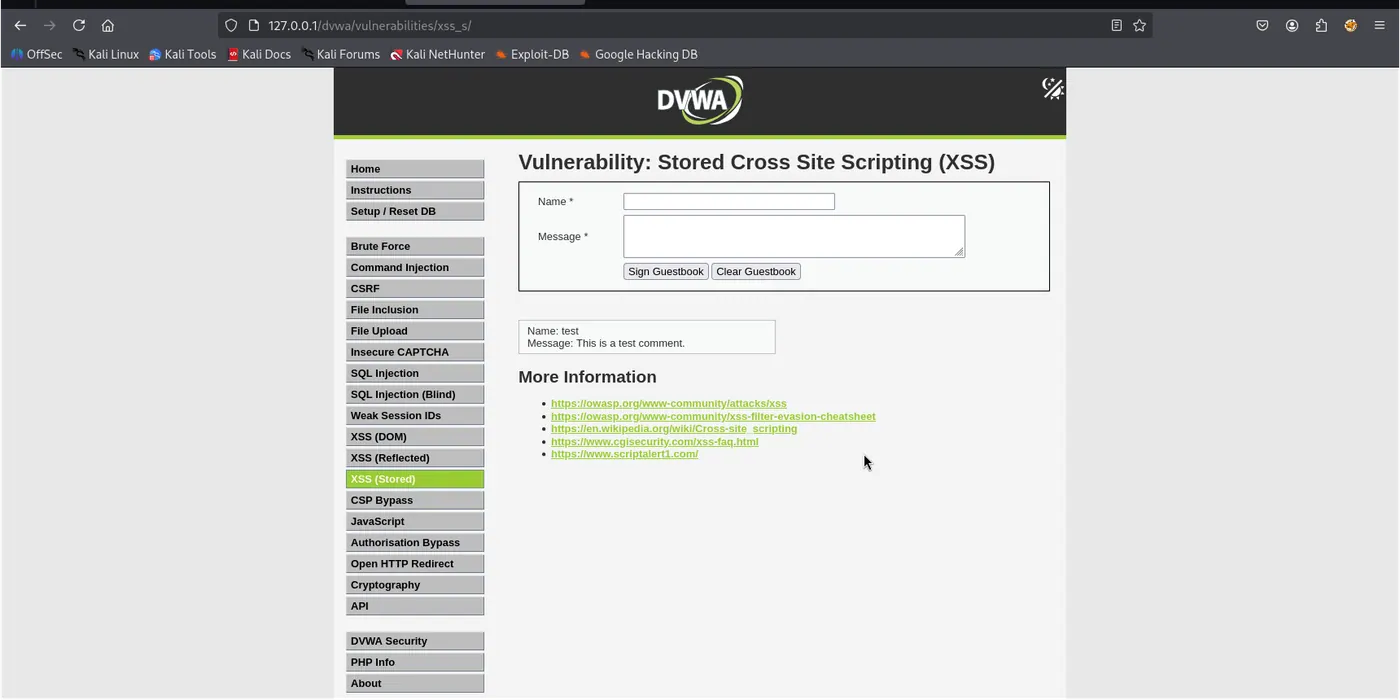
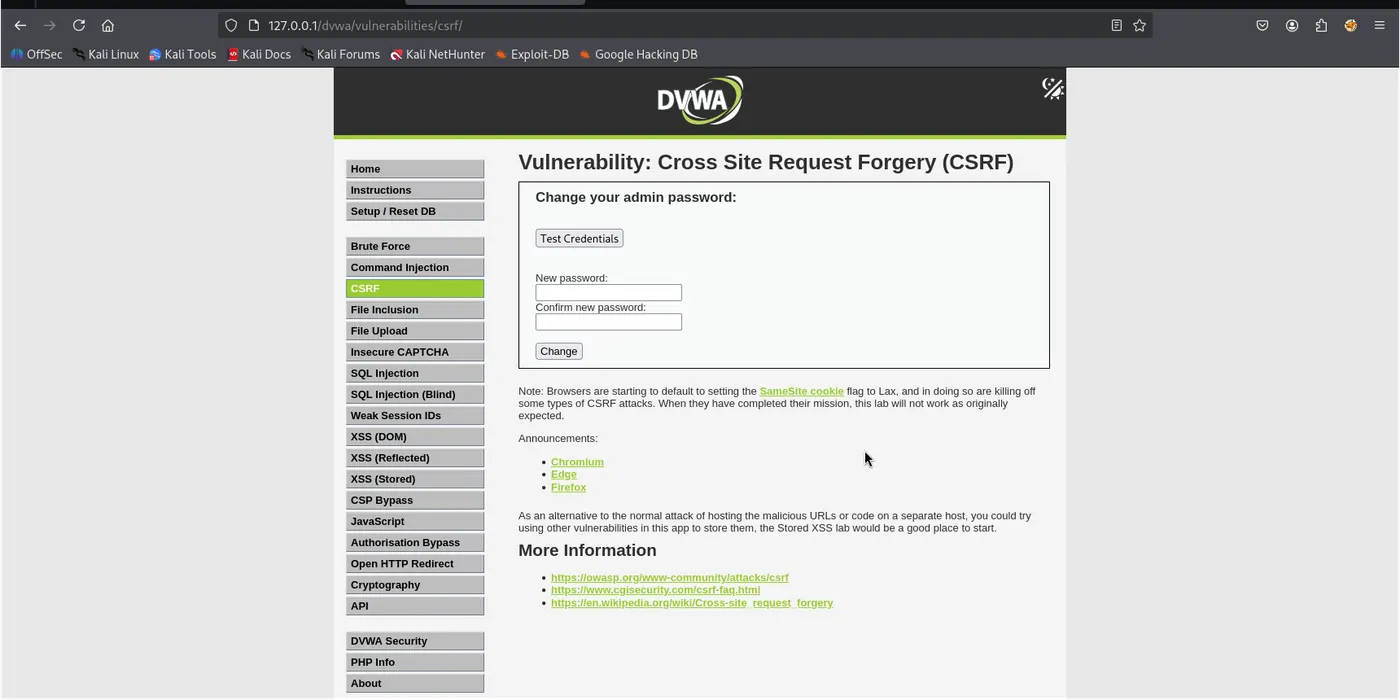
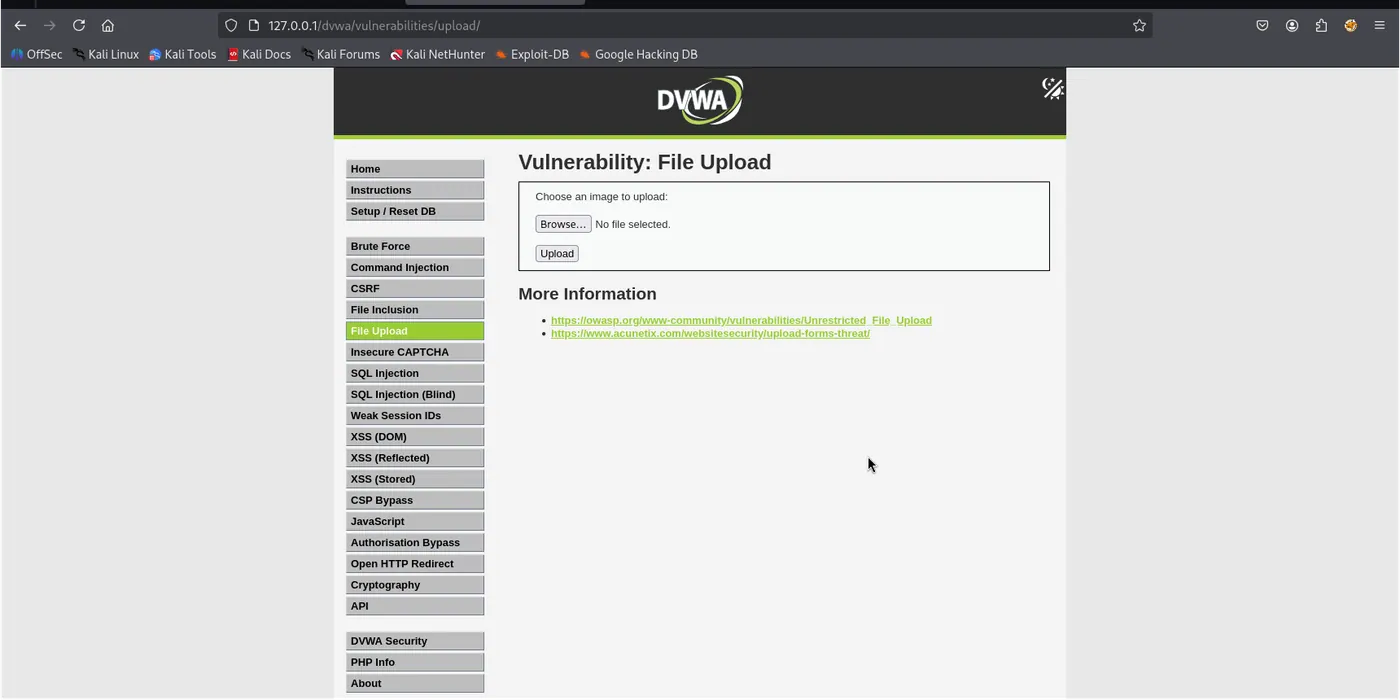
The lab uses intentionally vulnerable applications to practise SQL injection, XSS, CSRF, brute force, insecure upload, weak authentication and other common vulnerabilities. Each test can be documented with vulnerability description, impact, evidence and remediation.
Main Features / Lab Areas
Lab AreaLearning Outcome
SQL Injection
Understand database query manipulation
XSS
Understand client-side script injection
CSRF
Understand unauthorised request execution
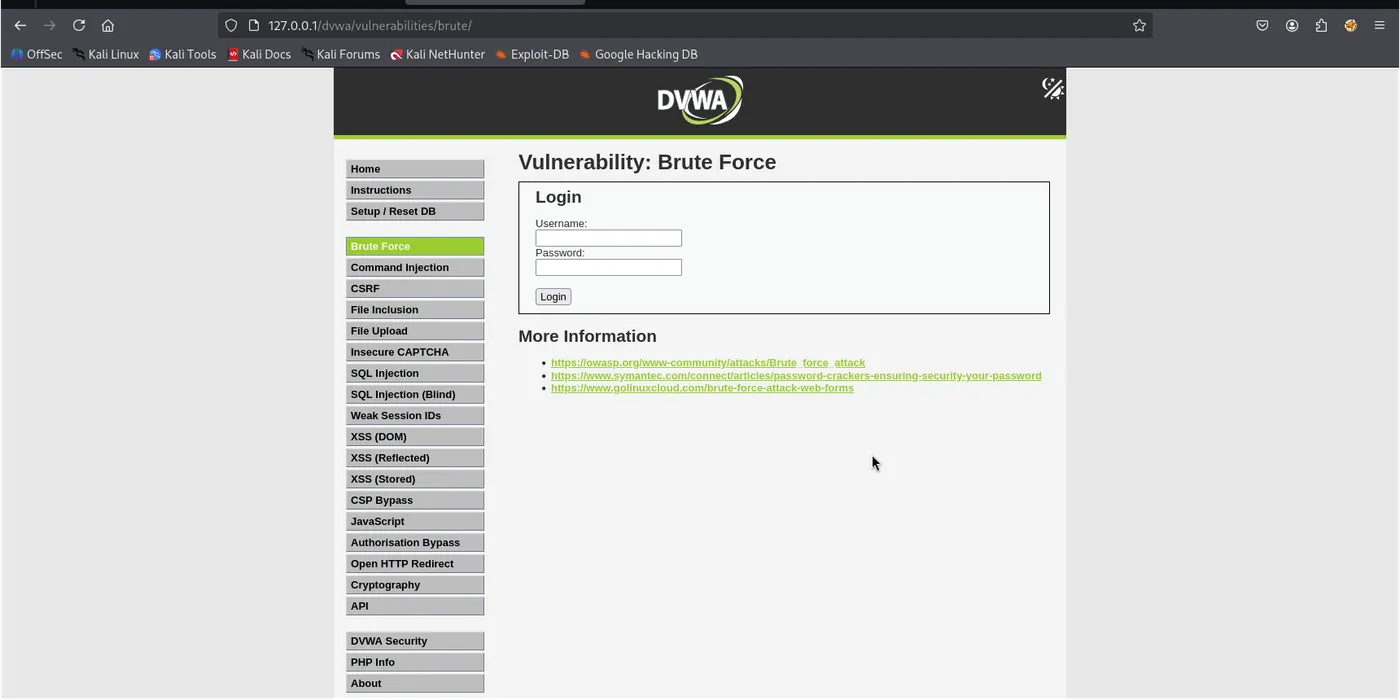
Brute Force
Understand weak login protection
File Upload
Understand unsafe upload risks
Security Levels
Compare low, medium and high defences
Reporting
Write professional vulnerability reports
Documentation Angle
This should become a cybersecurity lab report pack with each vulnerability documented as: objective, setup, method, evidence, risk rating, mitigation and reflection.